Release 0.5.1
Overview
AGS CLI 0.5.1 is a patch release on top of 0.5.0. Each item below is tagged with the area it affects: [Extend], [AMS], or [General].
Security assessment is also available from the Admin Portal. See the AGS 2026.5.1 release notes.
One change can break an existing script: ags ams upload now writes its result to standard output instead of standard error. See Improvements.
Highlights
[Extend] Security assessment for Extend apps (early preview)
You can request a penetration test for an Extend app's endpoints and download the report when it finishes.
ags extend security-assessment request --app my-app --namespace my-game
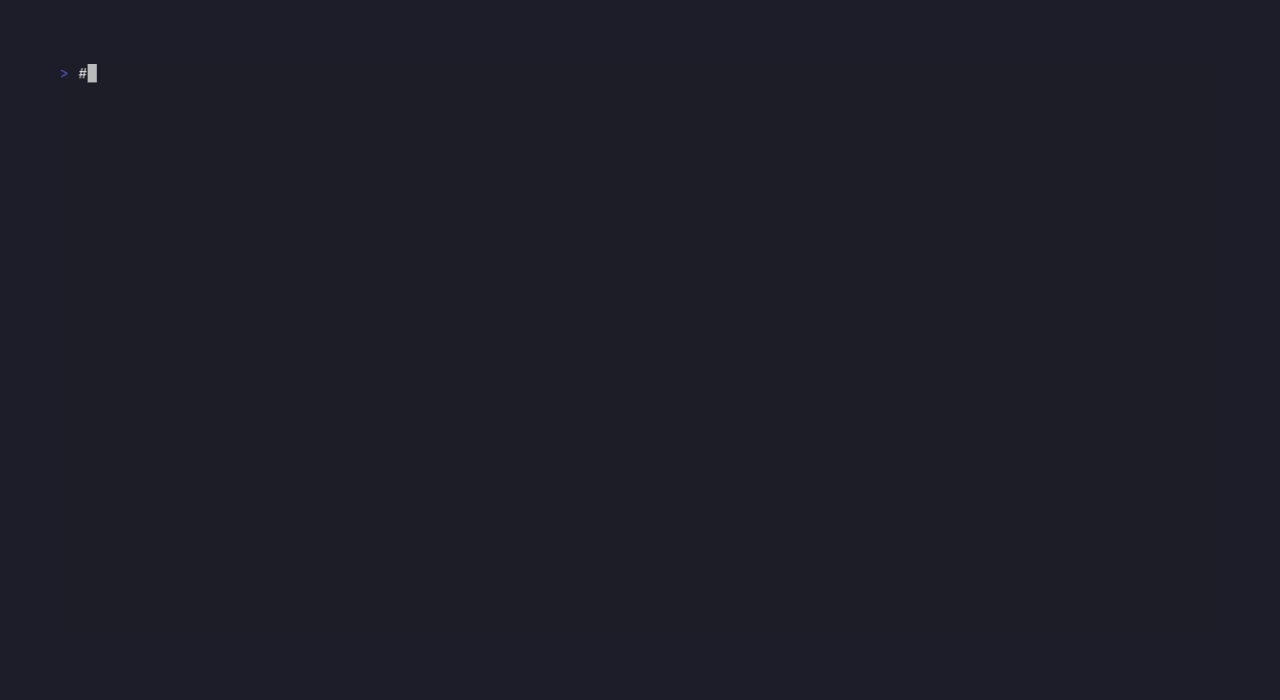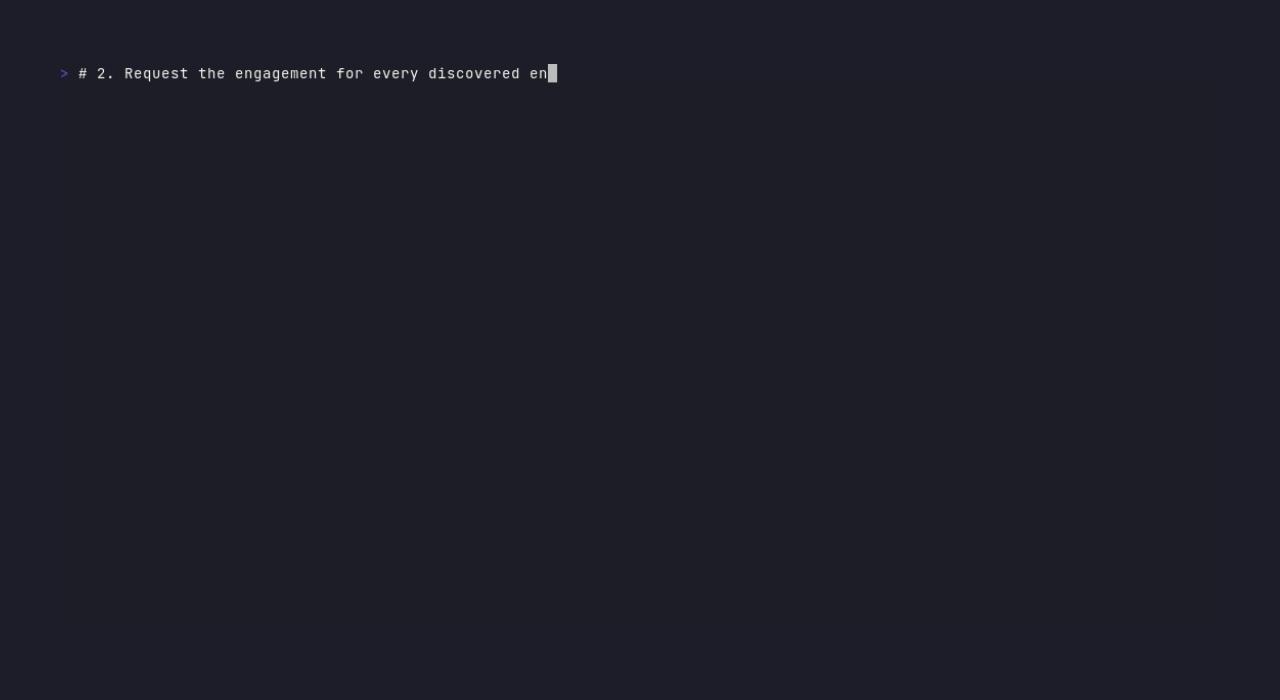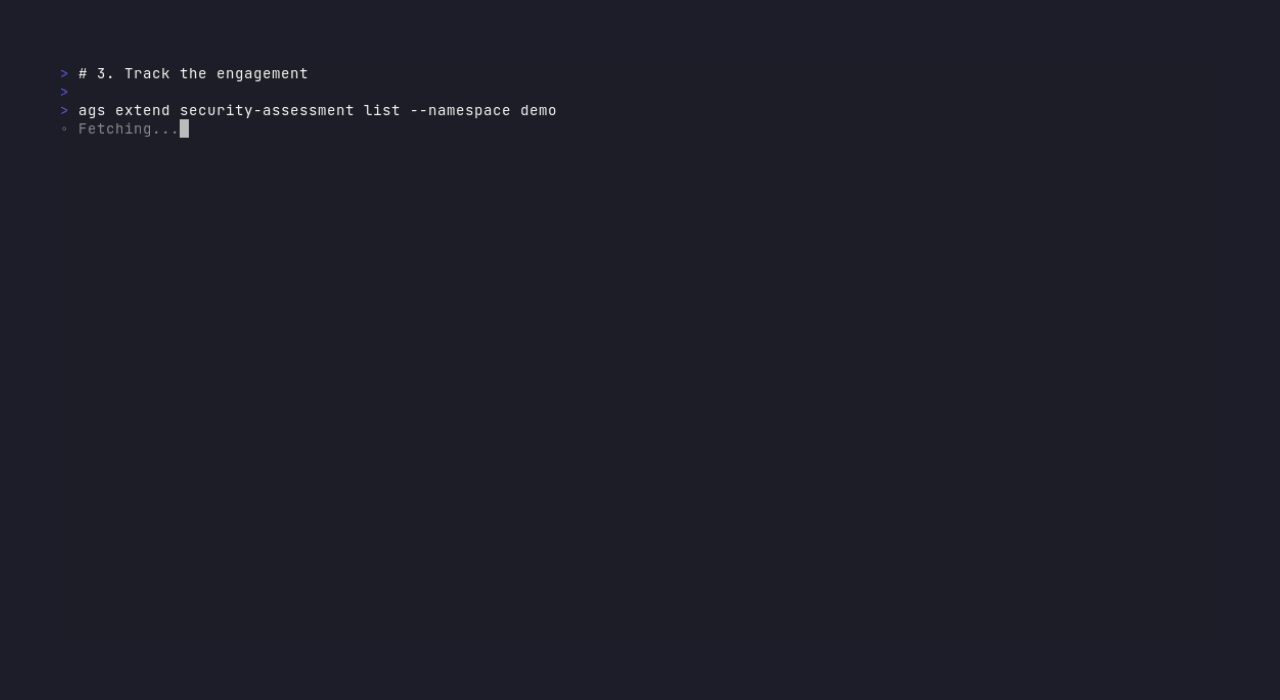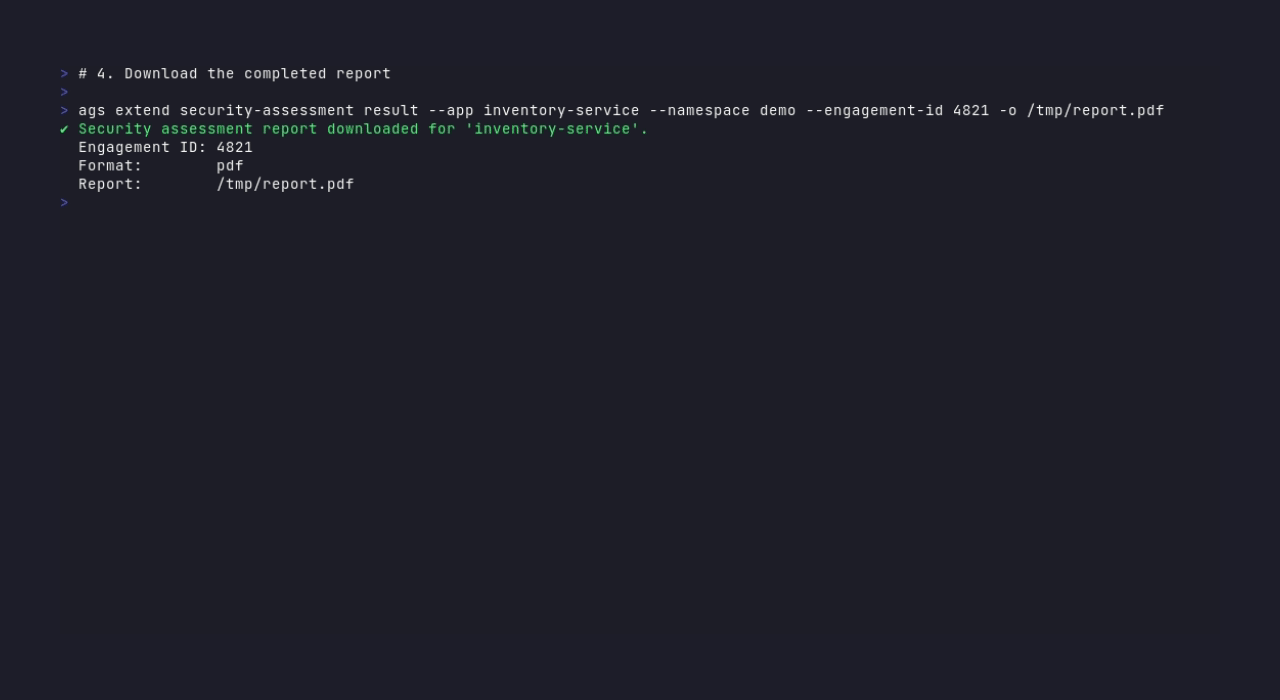
ags extend security-assessment result --app my-app --namespace my-game
request discovers the app's testable endpoints and lets you choose which ones to include. Pass --all-endpoints, or --operation-ids with a list, to skip the interactive checklist.
Endpoints that accept PUT, PATCH, or DELETE are listed and confirmed before the request is sent, because an assessment may generate test cases that modify or delete data through them. Pass --yes to confirm without a prompt, which a script needs.
Add --wait to block until the engagement reaches COMPLETED or FAILED. It polls every 10 seconds, up to --wait-limit seconds (default 1800). A wait that runs out of time exits with code 6, which is distinct from an API error (3), so a script can tell "the engagement may still finish" from "the server rejected it".
result lists the app's completed engagements, downloads the report as PDF or Markdown, and writes the file with owner-only permissions on macOS and Linux.
The app must be running, and CSM must have discovered an OpenAPI specification for it. The command needs a CSM version that provides the security assessment endpoints, so it is not available in every environment yet.
For what the assessment covers, how to prepare an app's endpoints for it, and the same workflow from the Admin Portal, see Request a security assessment.
[General] Update the CLI from the CLI
0.5.0 printed a note when a newer release existed. 0.5.1 adds the command that acts on it.
ags update             # reports whether a newer release exists, and prints the upgrade command
ags update --install   # upgrades this copy in place, after confirmation
ags update asks GitHub for the latest release and prints the one upgrade command that suits the way this copy was installed: the installer script, Homebrew, or a manual download. It changes nothing. Use --format json in a script.
ags update --install downloads the newest release's installer script and runs it for this copy. It asks for confirmation first, and --yes answers for a script. The previous binary is kept beside the new one and restored if the upgrade fails. A copy installed with Homebrew is refused, because Homebrew owns that installation, and ags update prints the brew command instead.
The CLI never updates itself unasked. Nothing happens until you type the command.
[General] Print the session token for another tool
ags auth token prints the current access token to standard output and nothing else, so another tool can reuse the session instead of running its own login.
curl -H "Authorization: Bearer $(ags auth token)" https://your-namespace.accelbyte.io/...
The token is resolved exactly as an API call resolves it, including a refresh when it has expired, so the printed token is the one the next request would send. It is written only to standard output, never to standard error, and never to telemetry. --format json adds the expiry and where the token came from.
Improvements
[AMS] ags ams upload writes its result to standard output
The result block, which carries the Image ID, architecture, entrypoint, archive size, and upload host, now goes to standard output. The Image "<name>" uploaded banner goes to standard error.
Until now it was the other way round, so ags ams upload ... > result.txt saved the banner and lost the Image ID. On a terminal the banner still appears before the result block, and --format json is unchanged.
Read the Image ID from standard output, not standard error.
[Extend] Wait for an app operation to finish (early preview)
ags extend create-app, deploy-app, start-app, stop-app, and delete-app accept --wait, which blocks until the operation finishes, with --wait-interval (default 10 seconds) and --wait-limit (default 600 seconds). This matches extend-helper-cli, so a migrated script keeps the same shape.
A wait that runs out of time exits with code 6, distinct from an API error (3), so a CI job can tell "it is still running" from "it failed".
[Extend] App lifecycle commands use the CSM v5 API (early preview)
deploy-app, delete-app, get-app-info, start-app, stop-app, and list-images now call the CSM v5 endpoints, and update-secret and update-var move with them. The v5 endpoints are the standard interface going forward, with consistent contracts across services and better transaction handling, and the legacy v2 endpoints they replace are being retired. The v5 endpoints use the same IAM permission resources as their v2 counterparts, so a role that worked before keeps working.
Upgrading refreshes your command catalogue for you. The CLI caches the catalogue and discards it when the CLI version changes, so nothing needs ags refresh-specs after the upgrade.
Smaller improvements
- [Extend]
ags extend <shortcut> --helpshows the shortcut's own help page, instead of a usage line for a command you did not type. - [AMS] The first progress line,
Validating <directory>, is written as a normal line on standard error, so a captured run shows it. It was previously a transient status update, which a terminal overwrote and a captured run dropped entirely. - [General] When a command exists at more than one API version, the output names the version it used. The label goes to standard error, so
--format jsonoutput stays unchanged for a script.
Bug fixes
- [Extend]
ags extend deploy-app --waitandstart-app --waitreport a failed rollout promptly when an app comes up and then crashes, for example from a bad image, a failed readiness check, or a crash loop. Until now the command waited out the whole limit and then reported a timeout. - [Extend]
ags extend deploy-app --waitconfirms the app is reporting the deployment it was asked to wait for, rather than any running deployment. - [AMS] Error messages quote the
--executablevalue as you typed it, instead of the resolved path. - [AMS] A 403 while finalizing or completing an upload says the identity is missing the
Updateaction ofAMS:UPLOAD, instead of implying the whole permission is missing. - [AMS]
ags ams upload --dry-runvalidates--upload-urlthe same way a live upload does, so an invalid value fails the dry run instead of being echoed back unchecked. - [General] The
DO_NOT_TRACKopt-out link points athttps://donottrack.sh. The previous domain serves unrelated content.
Full release notes
See the 0.5.1 release on GitHub for the complete list of changes.