Create a new role
Overview
This article contains information on how to create a new role in your environment using the AccelByte Gaming Services (AGS) Admin Portal or the AGS CLI.
The ability to customize your own roles in Public Cloud will be available soon.
Prerequisites
-
You have access to the Admin Portal and have sufficient permissions for roles management.
-
In Private Cloud, make sure you have the following permissions:
Usage Resource Action Create Role ADMIN:ROLECreate Add Role Permissions ADMIN:ROLEUpdate Invite User Admin ADMIN:NAMESPACE:{namespace}:USER:INVITECreate Admin Add User's Role ADMIN:NAMESPACE:{namespace}:ROLE:USER:*Update -
To follow the AGS CLI steps, you have installed the AGS CLI and signed in with an account that meets the requirements above. See Install and sign in. The examples use a Bash shell.
Create a new role
Follow the steps below to create a new role:
- Admin Portal
- AGS CLI
-
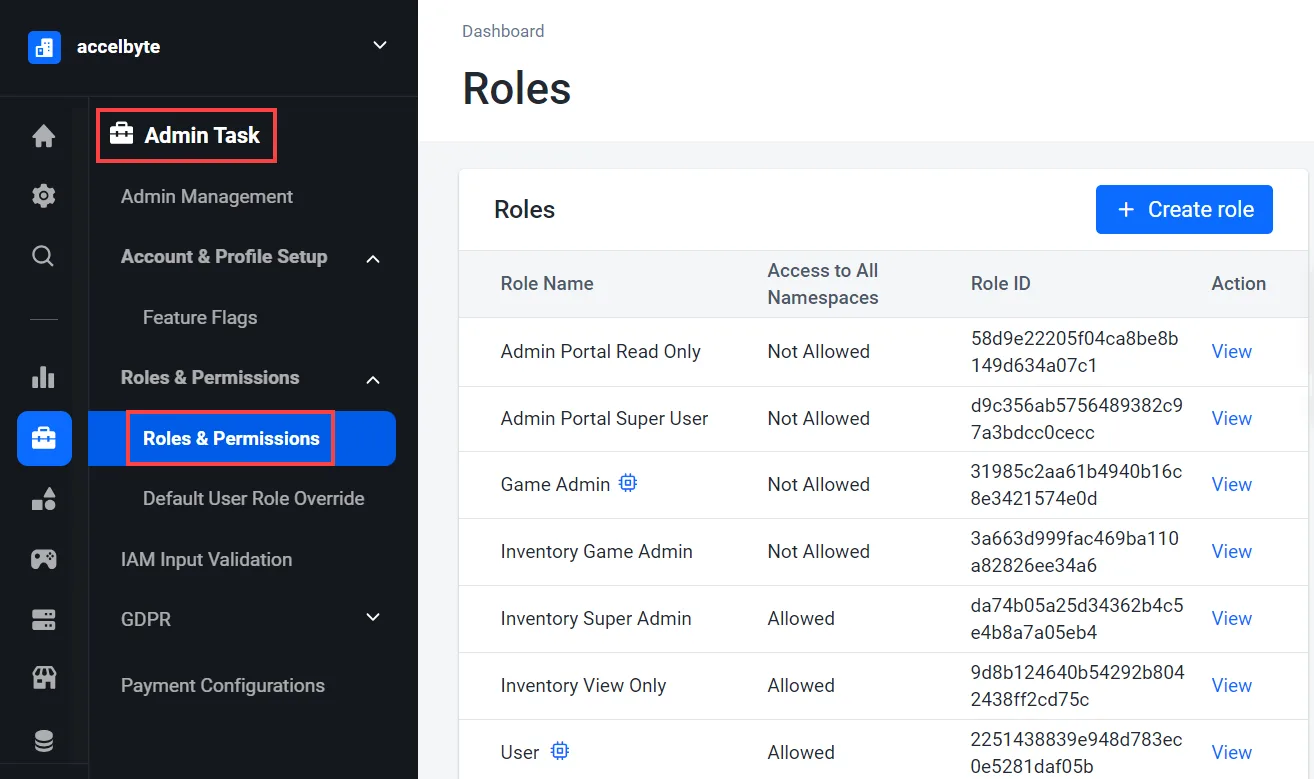
On the Admin Portal sidebar, go to Admin Task > Roles & Permissions.
-
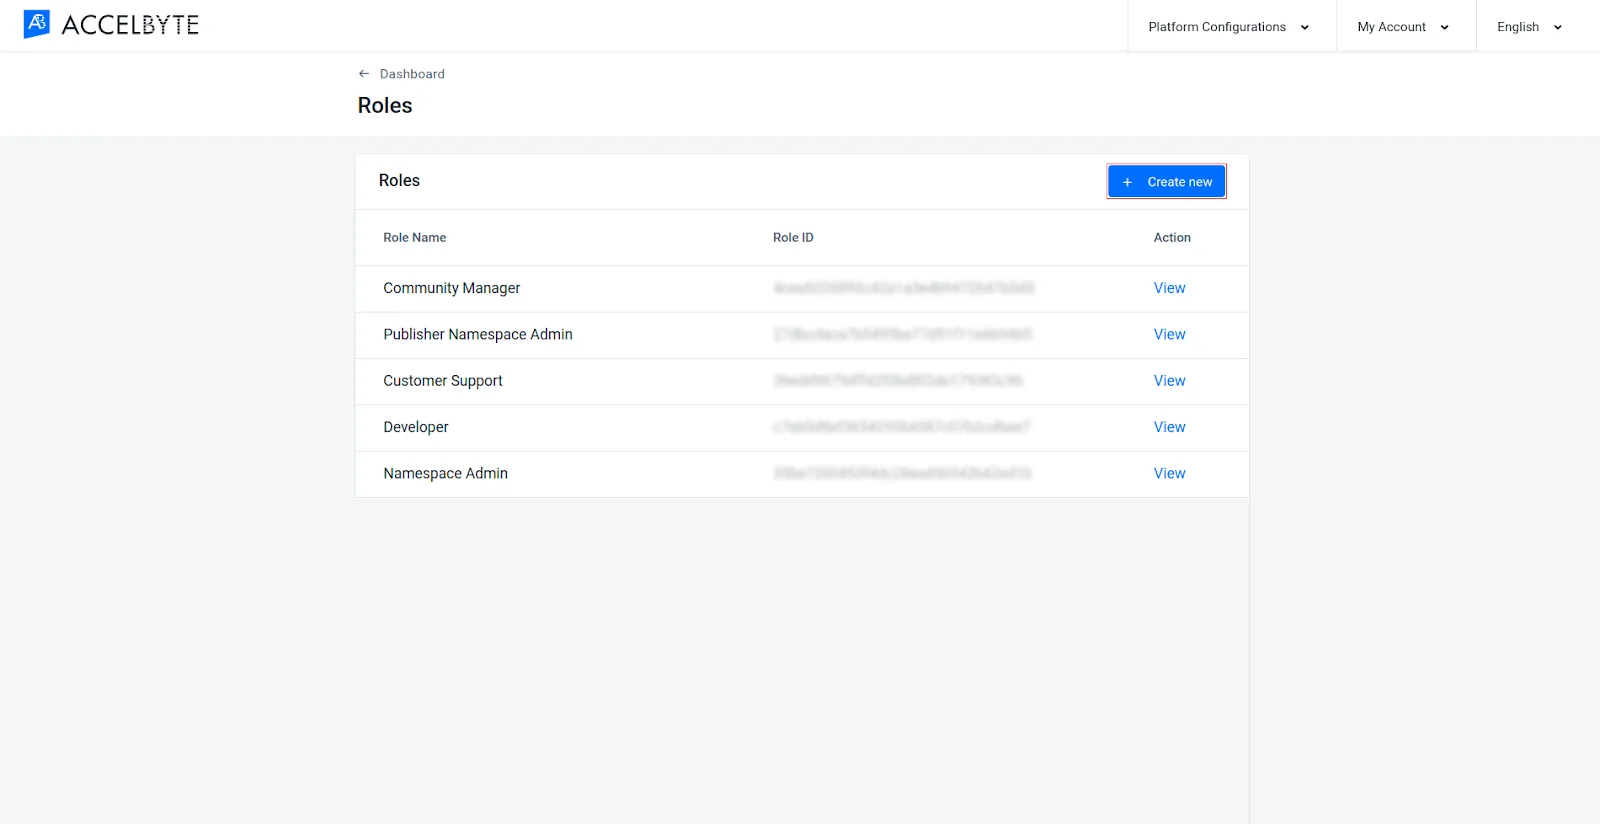
On the Roles page, click Create role.
-
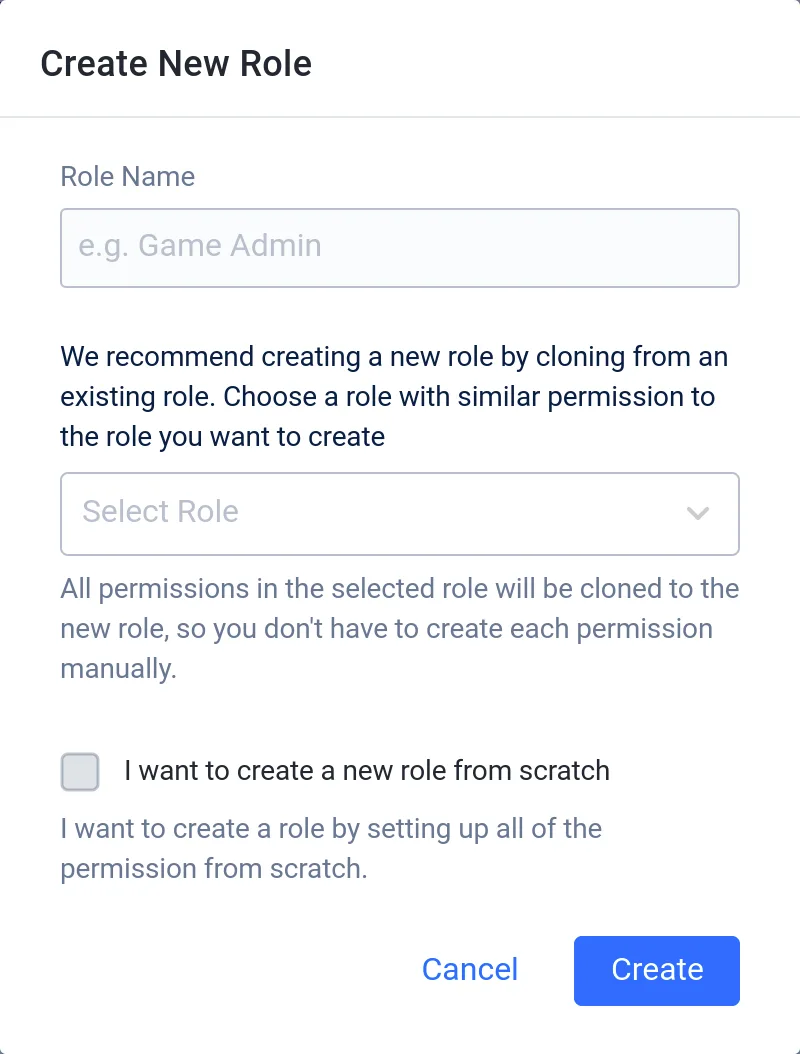
Choose whether to clone an existing role or to create a new role from scratch.
infoThe system default prompts you to clone an existing role. This enables you to quickly create new roles that carry over all the permissions from the cloned role.
-
To clone an existing role, fill in the Create New Role fields with the following information:
-
Type in a name for the role in the Role Name field.
-
Select the existing role that you want to clone from the Select Role dropdown.
-
-
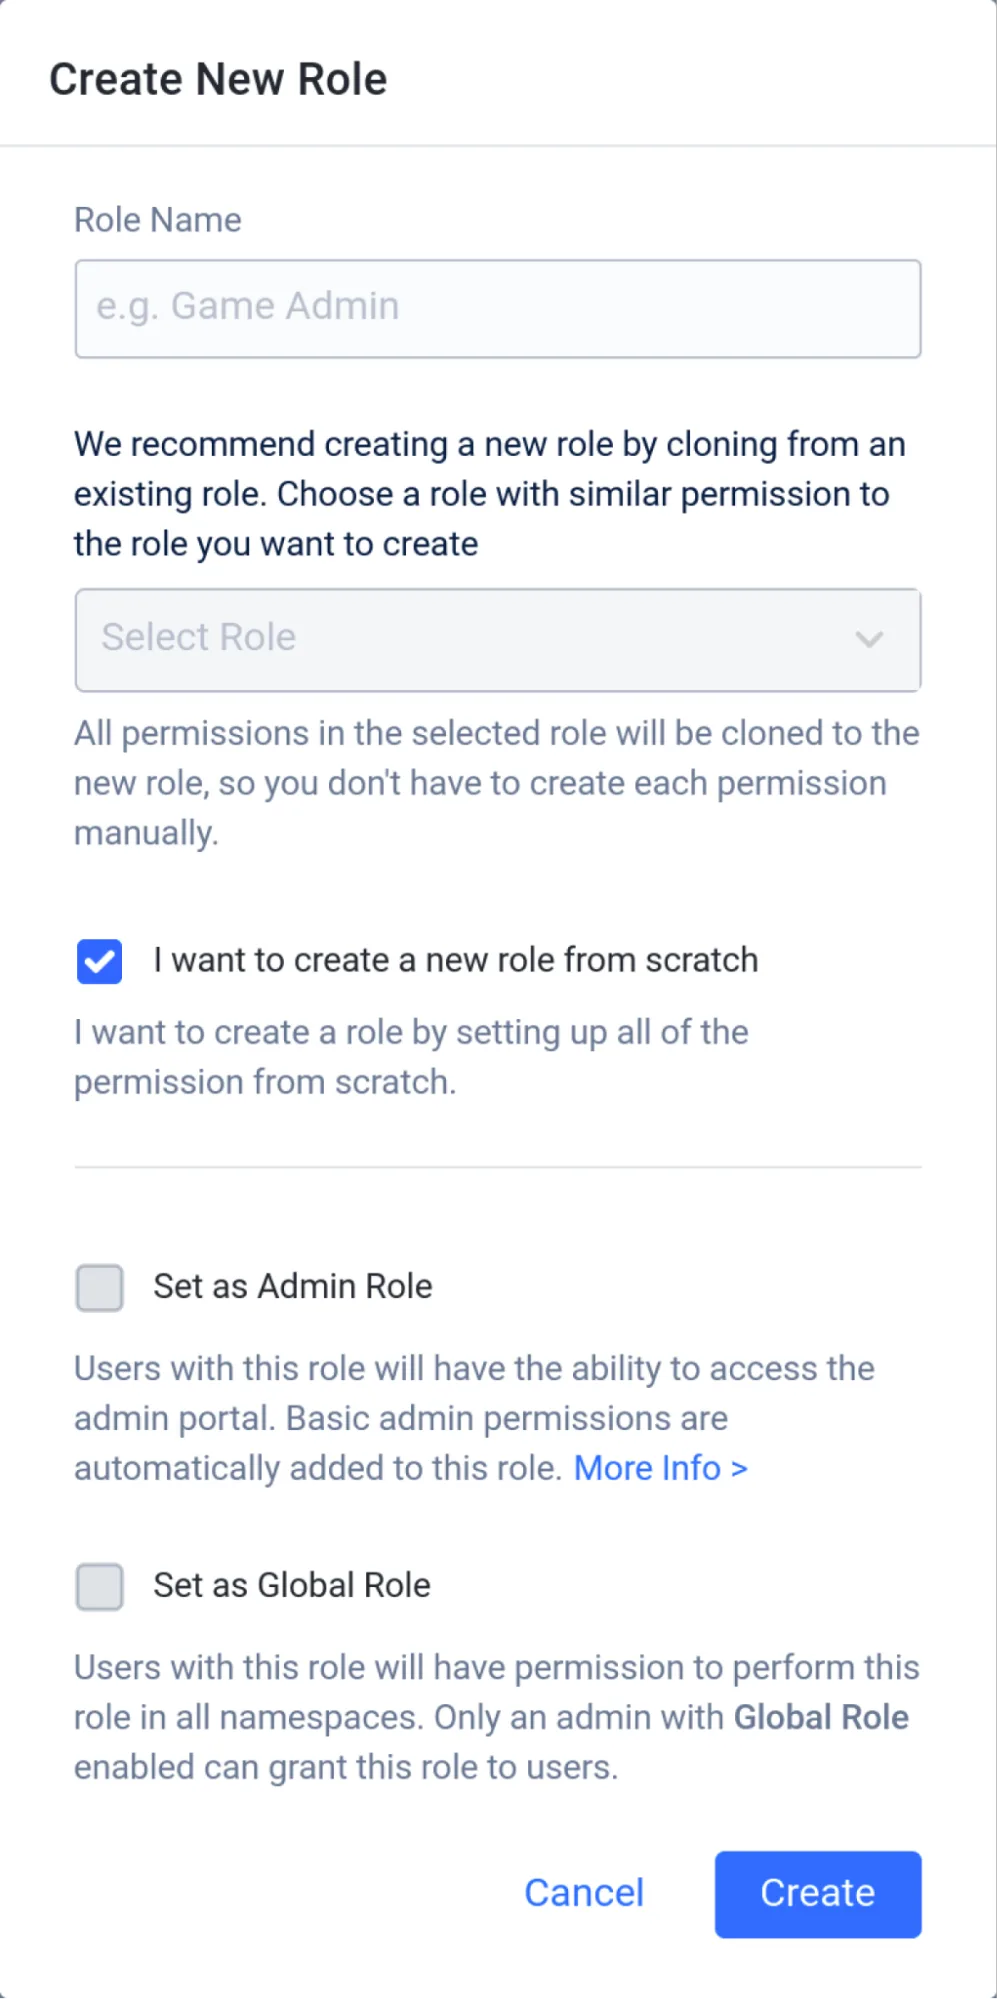
To create a new role without cloning, select the I want to create a new role from scratch checkbox and fill in the fields with the following information:
-
Type in a name for the role in the Role Name field.
-
Select the Set as Admin Role checkbox if you want your role to have access to the Admin Portal.
-
Select the Set as Global Role checkbox if you want your role to be able to access all namespaces.
-
-
-
Click Create.
-
Choose whether to clone an existing role or to create a new role from scratch. To clone a role, find the role that you want to clone. For each role, the output shows its
roleIdand its name (roleName). To create a role from scratch, skip to step 3.ags iam roles list --page-all --format json -
Save the role that you want to clone to a file. Replace
<SourceRoleId>with itsroleId. Any file name works. This example usessource-role.json:ags iam roles get --role-id <SourceRoleId> --format json > source-role.jsonNote the role's
adminRoleandisWildcardvalues, which you use in the next step. Then delete every field exceptpermissions. Don't change thepermissionslist, because these are the permissions that the new role gets in step 4. The file then looks like this, with one entry for each of the cloned role's permissions:{
"permissions": [
{ "resource": "ADMIN:NAMESPACE:{namespace}:USER", "action": 2 },
{ "resource": "ADMIN:NAMESPACE:{namespace}:ROLE:USER:*", "action": 4 }
]
}warningRemove
roleIdfrom the file. If the file still contains it, the command in step 4 adds the permissions to the role that you cloned instead of the new role. -
Create the role. Replace
<RoleName>with a name for the role, from 1 to 48 characters long:ags iam roles create --json '{"roleName": "<RoleName>", "adminRole": false, "isWildcard": false}'adminRole: the Set as Admin Role checkbox. Set it totrueto give the role access to the Admin Portal.isWildcard: the Set as Global Role checkbox. Set it totrueto let the role access all namespaces.
When you clone a role, use the values that you noted in step 2, the same as the Admin Portal does. The output shows the new role's
roleId. -
Add permissions to the new role. Replace
<NewRoleId>with theroleIdfrom step 3.-
If you cloned a role, add the permissions from the file that you edited in step 2. If the
permissionslist is empty, skip this step.ags iam roles add-permissions --role-id <NewRoleId> --json @source-role.json -
If you created an admin role from scratch, add the Read permissions that the Admin Portal adds to every admin role it creates. Create a JSON file with this content. Any file name works. This example uses
admin-permissions.json:{
"permissions": [
{ "resource": "ADMIN:ROLE", "action": 2 },
{ "resource": "ADMIN:NAMESPACE", "action": 2 },
{ "resource": "ADMIN:NAMESPACE:{namespace}:NAMESPACE", "action": 2 },
{ "resource": "ADMIN:NAMESPACE:{namespace}:CONFIG:COMMON", "action": 2 }
]
}Then add the permissions:
ags iam roles add-permissions --role-id <NewRoleId> --json @admin-permissions.json -
If you created a role from scratch that isn't an admin role, skip this step.
-
You've successfully created a new role in your environment. You can now add permissions to it or assign in to a user.